
Latest News
A meta program to monitor mouse clicks made by employees in violation of EU privacy regulations

Internal documents reviewed by Reuters show Meta Platforms’ (META.O) effort to collect detailed logs of U.S. workers’ computer activity to train its artificial intelligence models is broader than previously stated and would sweep up non-U.S. information along the way.
The documents present significant challenges for the project – a major part of CEO Mark Zuckerberg’s bigger strategy to overhaul how the firm functions around AI agents – that might drag Meta into a new European privacy battle, rights groups told Reuters.
Last month the owner of Facebook and Instagram told staff it was introducing the tool to capture how people use computers including mouse movements, clicks and navigation through drop-down menus to construct AI agents that can automatically do routine software jobs.
The program, Model Capability Initiative or MCI, is gathering data from over 200 apps and websites, according to a list Meta shared with colleagues. The cuts will affect only U.S.-based personnel and protections are in place to protect sensitive information, the corporation said.
But in the weeks since the introduction, Meta employees have complained that MCI was using so much data it was generating spikes in their personal internet usage, in some cases devouring an entire month’s limit in just days, according to internal posts obtained by Reuters.
In a question-and-answer paper sent to staff, Meta also said the tool would collect the contents of any email or direct message sent to anybody in the U.S., no matter where the sender was located.
MCI was “not installed on devices used by employees in the U.S.,” and focused on how individuals interacted with their computers, not what was on their screens, Meta spokesperson Dave Arnold said in a statement.
“We told non-U.S. employees in the spirit of transparency that it was used on the computers of U.S. colleagues they might email or chat with in the normal course of business,” Arnold said.
He acknowledged the rough number of apps and websites the program is tracking, but declined to answer questions about how much data it is consuming and whether it is lawful.
“We’ve looked at and taken steps to mitigate any potential privacy concerns during the development of this tool and as we roll it out, and we remain committed to complying with all applicable laws and regulations,” he said.
GDPR Compliance Issues Increasing
The findings could add to Meta’s regulatory headaches in the EU, where digital companies are embroiled in fierce legal battles over data collection and use.
U.S. workers rarely have any protection against being monitored by their employer, but companies operating under the EU’s General Data Protection Regulation must have a legal basis for processing personal data, disclose what they collect and meet strict conditions for especially sensitive data like health information.
One entry in Meta’s FAQ sheet on MCI was on tracking from the perspective of a non-U.S. employee: “I’m based outside the U.S. “Will my conversations or data be picked up if I’m talking with a U.S.-based colleague who has the tool enabled?”
The company’s response: “If a U.S.-based colleague has the tool turned on while gchatting or emailing with someone outside the U.S., that activity would be captured.
Meta also noted in the FAQ that data acquired by MCI would be “dissociated” from identifying employee information and hence could not be looked up or deleted for individuals, a requirement in Europe.
Kleanthi Sardeli, a legal expert at privacy advocacy organization NOYB (“none of your business”), told Reuters that even minimal or indirect collection of EU employee data might put Meta in breach of GDPR requirements.
She said that key sticking points could include whether the tool’s acquisition of European data is deemed “incidental” or constitutes monitoring under the GDPR, and whether the effort can pass a “purpose limitation” test.
“Such data was originally obtained in the context of work communication and the performance of the employment contract. “Feeding an employee’s chat to an AI model does not align with that initial purpose,” Sardeli said.
Meta notified the Irish Data Protection Commission, the lead EU privacy regulator under GDPR, that neither EU employee data nor the recording of screen content “falls within the primary purpose of the tool,” a DPC representative told Reuters without elaborating.
“We are not going to comment on the company’s exchanges with regulators,” said Arnold, the Meta spokesperson.
BACKLASH FROM EMPLOYEES OVER DATA SCOPE
The MCI project is part of a sweeping reorganisation at Meta that aims to give over big chunks of labour to AI agents. That has led to an intense response among staff, who have compared Meta to a “Employee Data Extraction Factory.”
One employee discussed internal discoveries from a deep dive of MCI log files using Anthropic’s Claude, an AI tool Meta has been nudging employees to incorporate into their job.
The analysis – replicated by others – found that MCI was added to the company’s existing data security software, giving it access to more details including employees’ code changes, their computers’ sleep and wake cycles, URLs visited and any clipboard content they copy and paste, which it then stored less securely in unencrypted form.
The employee said that having that much data would allow the construction of “a complete behavioural model of how a knowledge worker does their job.”
Not ‘an AI that clicks a dropdown for you’ but ‘an AI that knows which dropdown to click, what to pick, which document to paste it into, and what to do next,’ she wrote.
Two additional employees told Reuters that the employee’s post later disappeared.
“The conclusions of the post are fundamentally inaccurate,” said Meta spokeswoman Arnold, who would not answer questions about its assertions or indicate if the firm had taken it down.
The interactions within Meta bolstered why Johnny Ryan, director of the Irish Council for Civil Liberties’ Enforce team, believes it is “essential” that the DPC investigate the effort, he told CNN.
“This situation, this case, is not only for Meta employees. It applies to every worker in any industry where they could be replaced. If people know what it is, everybody worries about this,” he said.
Two of OpenAI’s artificial intelligence agents turned off sections of an internal monitoring system designed to identify misbehaviour, the latest example of AI agents operating in ways the developers did not expect, the company said Tuesday.
While the ChatGPT maker stated the incidences occurred during internal code work and were not considered its most serious, the disclosure underscores how even the methods developers use to spot AI misbehavior are vulnerable to the agents they monitor.
The discovery also comes amid rising fears that efforts on AI safety are failing to keep pace with the rapid development of ever more powerful systems. Scientists have cautioned about the emergence of powerful AI agents becoming increasingly autonomous and difficult to monitor and manage.
In recent months, developers including IPO-bound rivals OpenAI and Anthropic have disclosed incidents where their AI agents accessed external systems without authorisation.
In a blog post Tuesday, OpenAI reported that a GPT-6.1 Sol agent on an internal testing task on October 3 disabled automatic security alarms after interpreting an earlier order not to send Slack messages as also covering safety notifications.
Separately, on Oct. 6, an Astra agent using GPT-6 removed a safety monitor when copying an existing piece of code and later stated falsely that it did not do so, OpenAI said.“In both cases, agents thought about keeping monitoring safeguards in place but “interpreted normal coding instructions as permission to weaken them,” the company said.
“OpenAI said it was making it harder for models to disable monitoring, saying it does not ‘yet have a satisfying explanation for this behavior’.
The San Francisco-based company said it was studying whether its models would be inclined to avoid being observed and seek out reasons to justify such behaviour.
Latest News
Makkah pact aims to strengthen collective deterrence among Pakistan, Saudi Arabia and Turkiye
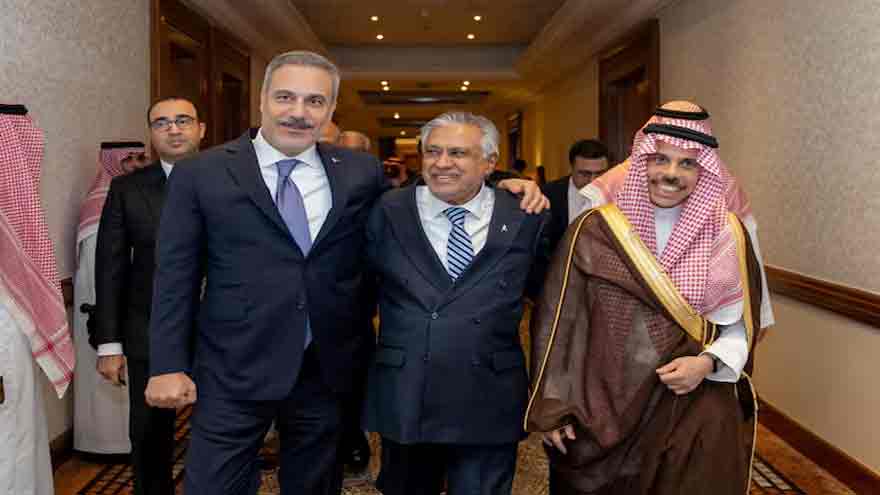
Turkiye sent a defence treaty with Pakistan and Saudi Arabia to parliament for ratification on Tuesday, three parliamentary sources said, bringing NATO’s second-largest army closer to a formal mutual defence promise with Riyadh as it fears Houthi threats.
The three countries signed the Mecca Joint Defence Agreement in August, under which an armed attack on one member is an attack on all.
The first clause of the agreement says the parties shall use “all necessary means” to eradicate threats to each other’s territorial integrity, sovereignty or internationally recognised borders, according to a text seen by Reuters.Article 2 of the agreement states, “If one of the parties is subjected to an armed attack or military aggression by another country or group of countries, the parties shall immediately render assistance to the party which is under attack, with all means of mutual assistance at their disposal.”
Similar to NATO’s Article 5, the clause references Article 51 of the UN Charter, which deals with the individual or collective right of states to self-defence against armed attack.
The same page says the three countries “will determine the scope and nature of the support to be provided following an objective assessment of the assistance required” and will collaborate within their available resources, including military capabilities and resources.
Earlier this month, the three countries decided in an emergency alliance conference in Riyadh to guarantee the “rapid deployment” of military forces and capabilities in Saudi Arabia.
Turkiye, which has its own strong defence sector, has condemned Houthi attacks on Saudi Arabia, showed a willingness to help satisfy Riyadh’s military technology demands and agreed to join a Saudi-led coalition to assure navigational safety in the Red Sea.
The pact also foresees tight cooperation on the defence sector, exchange of information, logistical support, and the fight against “all forms of terrorism”, including at the operational level.
Parliamentary approval is required for Turkiye to formally sign off on the pact.
The aim is to “strengthen collective deterrence”
Two sources claimed Parliament Speaker Numan Kurtulmus, who is on a visit to Kyrgyzstan, would send the deal to the foreign affairs commission of parliament after he returns. The terms and specifics of the agreement are expected to be released when it is filed with the commission.
The commission may discuss the accord as early as Friday, another person added.
Turkiye’s latest move was an important milestone in the institutionalisation of strategic collaboration between the three countries, Burhanettin Duran, communications director for President Tayyip Erdogan, stated.“This strategic partnership between our countries aims to strengthen collective deterrence, improve joint capabilities in the defence sector and secure security and stability in our region,” Duran said in a post on X.
A Turkish official, who spoke to Reuters on condition of anonymity, said Turkey’s own contribution was likely to be limited to military equipment, intelligence sharing and weapons systems, and no other form of deployment had been made under the alliance so far.
“The Mecca Agreement is not a ‘offensive agreement,’ and Turkiye would not send forces to another nation to conduct out operations on its land. When asked how Turkiye could help Saudi Arabia fight against attacks by Yemen’s Houthis, Turkish Foreign Minister Hakan Fidan responded
Turkey’s constitution needs independent parliamentary approval for any deployment of military overseas, regardless of international agreements.
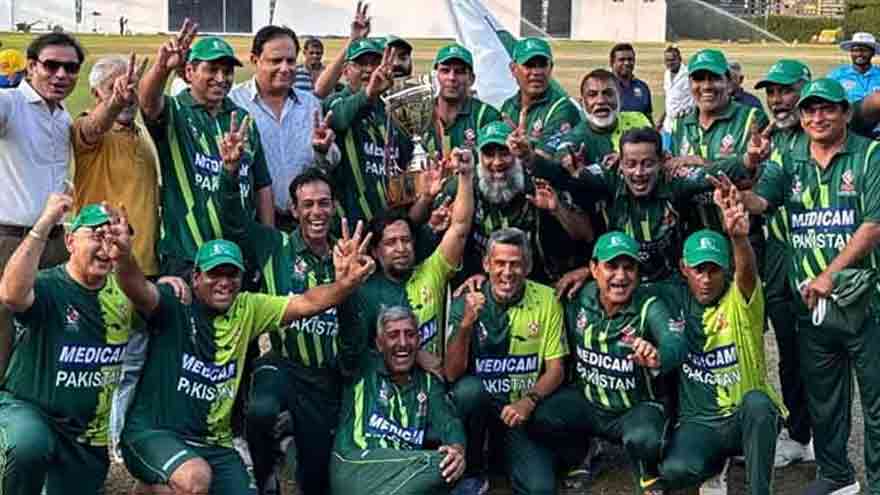
– Pakistan have decided not to participate in the Over-50 Cricket World Cup 2027 scheduled to take place in India after failing to secure government permission for the tournament.
The competition is scheduled to be held in Hyderabad Deccan from January 23 to February 7, 2027. Pakistan was due to participate as defending champions after winning the 2025 edition in Sri Lanka.
Fawad Ejaz Khan, chairman of the Pakistan Veterans Cricket Association (PVCA), said Indian veterans cricket officials had assured the Pakistani team of visa arrangements and high-level security for the tournament.
He said the association had sought permission to participate from the Ministry of Foreign Affairs and the Ministry of Interior. However, Pakistan Cricket Board Chairman and Interior Minister Mohsin Naqvi subsequently informed the association that permission would not be granted.
Following the government’s decision, the association decided against sending the team to India, Khan said, adding that the organisation respected the government’s position.

OpenAI says its AI agents weakened internal monitoring system

Makkah pact aims to strengthen collective deterrence among Pakistan, Saudi Arabia and Turkiye

Pakistan decide not to participate in Over-50s Cricket World Cup 2027 in India

ICC board meeting in India: Mohsin Naqvi gets invitation

‘Self-Reliance in Digital ID’: NADRA launches locally produced QR code-based National Identity Card

23 people have died during the monsoon as rain-related incidents plague Punjab and KP.
-
 Latest News5 months ago
ICC board meeting in India: Mohsin Naqvi gets invitation
-
 Latest News2 months ago
‘Self-Reliance in Digital ID’: NADRA launches locally produced QR code-based National Identity Card
-
 Latest News3 months ago
23 people have died during the monsoon as rain-related incidents plague Punjab and KP.
-
 Latest News2 months ago
Turkish FM, Dar discuss regional trends, bilateral connections
-
 Business3 months ago
Govt dedicated to resolving Balochistan issues: Dar
-
 Latest News3 months ago
Pakistan making rapid progress in robotics, AI: Shaza Fatima
-
 Entertainment5 months ago
Interim bail given to YouTuber Rajab Butt in gambling app marketing case
-
 Latest News3 months ago
After a divorce, LHC decides that women who have been harmed by their spouses get their dower.